Summary
- Hyperliquid said the XMR1 token fell from about $500 to $1, marking a 99.8% decline.
- Bitquery said a wallet that received 5.2 million tokens from the XMR1 deployer account sold them, triggering a $13.5 million large-scale selloff, and then converted and moved the proceeds into USDC and ETH.
- PerpetualCow raised the possibility of a security breach at hosting provider 1984 and suspected private-key exposure, and said he would compensate losses suffered by affected traders.
Forecast Trend Report by Period
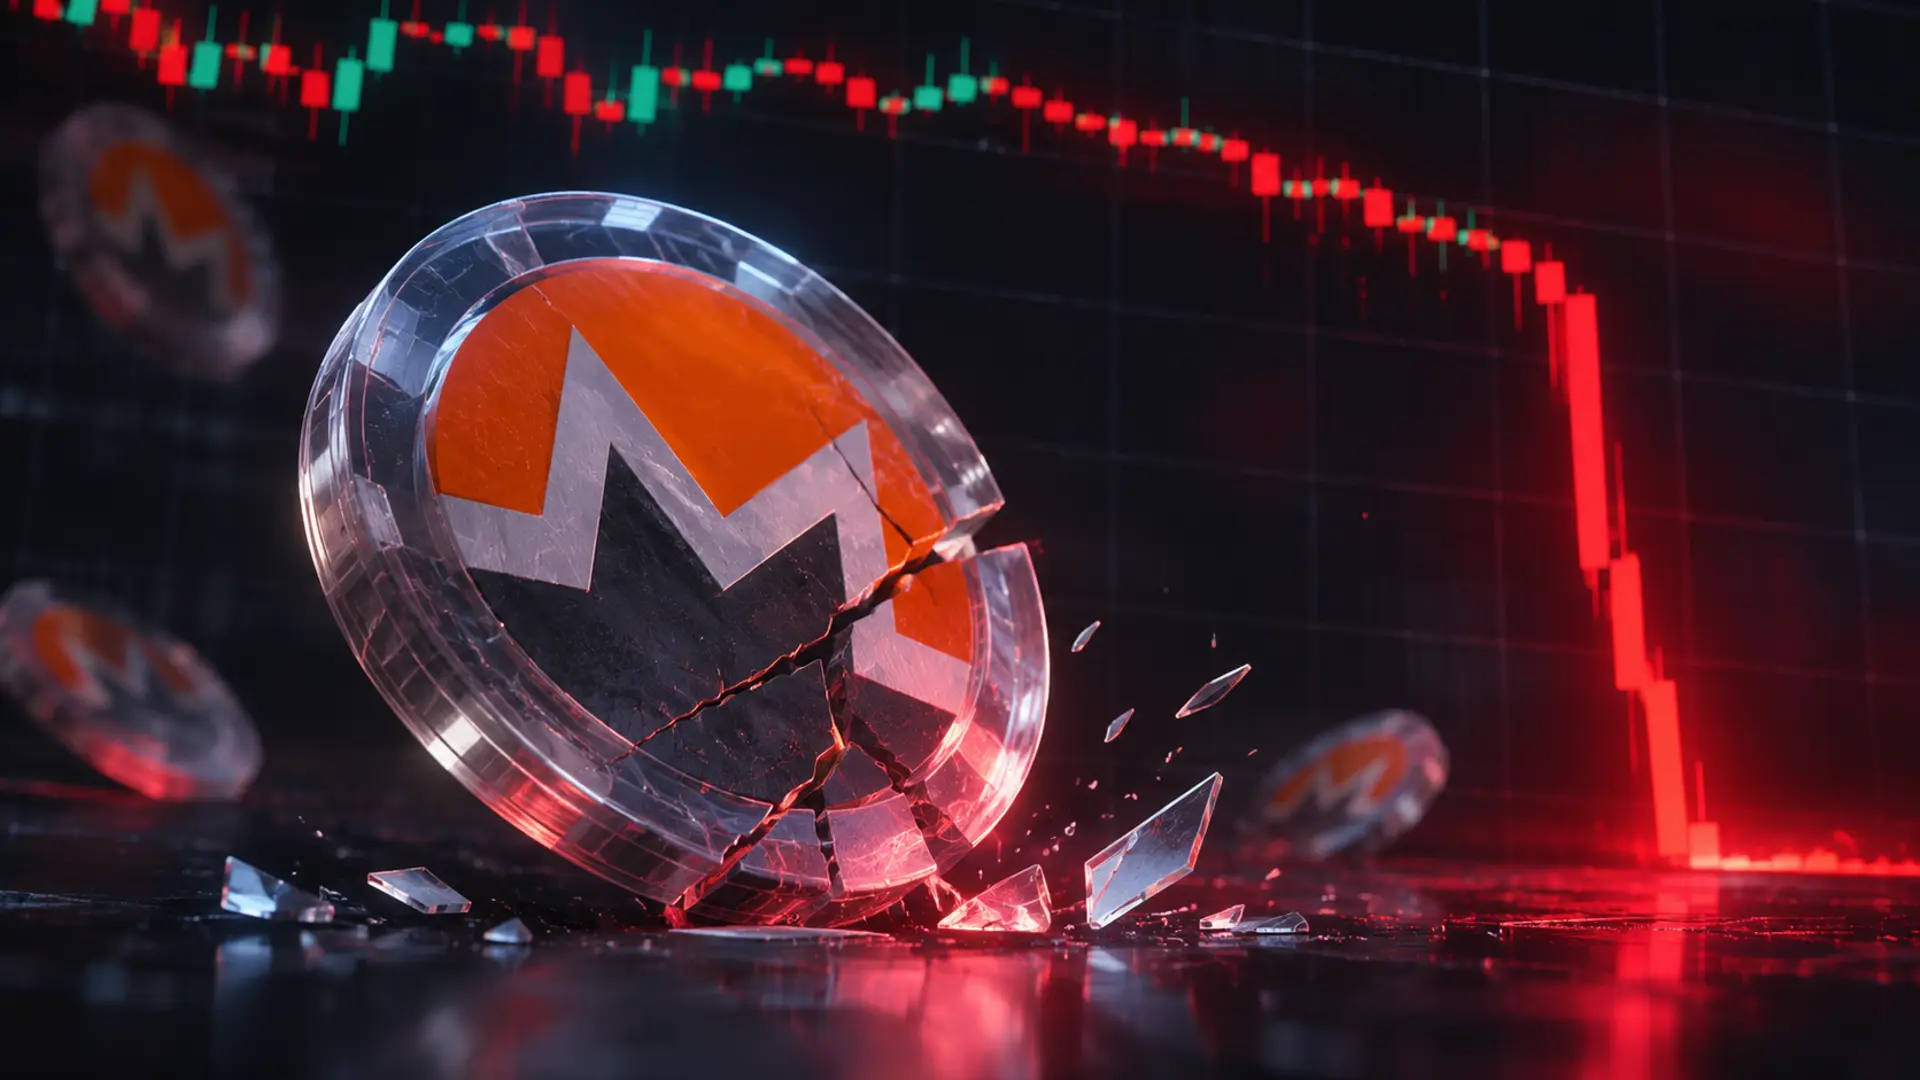
The wrapped Monero token XMR1 plunged more than 99% in 30 minutes on decentralized trading platform Hyperliquid after a large selloff hammered the market.
Cointelegraph reported on November 20 that blockchain analytics firm Bitquery said XMR1 traded on Hyperliquid fell from about $500 to $1, a drop of 99.8%. XMR1 is a wrapped token designed to allow Monero to trade on other blockchains. The collapse occurred in XMR1, not in the original Monero asset.
Bitquery’s on-chain analysis showed that a wallet that had received about 5.2 million tokens from the XMR1 deployer account sold roughly $13.5 million worth, triggering the price plunge. The wallet then moved about $13.28 million in USDC from the sale to the Arbitrum network.
About $13.22 million of the funds transferred to Arbitrum was later swapped for 7,467 Ether through decentralized trading protocol CoW Protocol. Most of that Ether was then sent to the Ethereum mainnet.
Bitquery also found signs that about $6.6 million tied to four hacks earlier this month involving Across Protocol, Kava, Li.Fi and Safe was used to buy XMR1. It added that there was no on-chain evidence confirming a direct link between those hacking incidents and the latest large selloff.
The cause of the incident has not been clearly identified. Bitquery said it could not determine how the private key for the XMR1 deployer account may have been exposed or who controlled the account when the token transfer took place.
PerpetualCow, the operator of XMR1-related service Wagyu, raised the possibility of a security breach at hosting provider 1984. The operator said customer data and internal server files at the company had been exposed externally, and records from a server that had previously stored the XMR1 deployer’s private key may have provided a path for the leak.
According to the operator, the server that stored the private key had already been deleted. Even so, related logs and files may still have remained with the hosting provider. Whether there was an actual security breach and how the private key was exposed have not been independently verified.
PerpetualCow said he would personally compensate traders who suffered losses in the incident. He also said the Wagyu service would be relaunched, though no detailed timetable or compensation plan was disclosed.
Suehyeon Lee