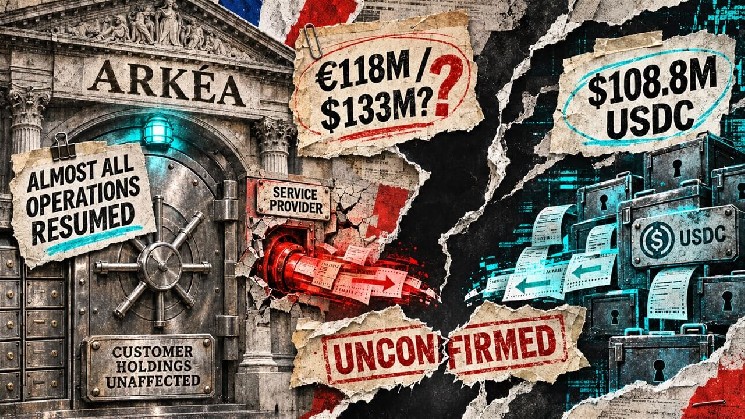
Crédit Mutuel Arkéa, a French regional bank, was hit by a cyberattack that stole approximately €100 million (approximately $112.7 million) of its own funds. Just days after roughly 8 trillion won (approximately $6.0 billion) was drained from Binance, the world's largest cryptocurrency exchange, traditional finance has also become a target, showing that the security crisis surrounding digital assets is spreading across industry boundaries.
According to Agence France-Presse, Crédit Mutuel Arkéa disclosed on the 4th (local time) that hackers accessed bank accounts and siphoned funds out. The bank did not disclose the exact amount of damage, but local outlet Le Télégramme reported the stolen amount at around €100 million. The bank said only its own accounts were affected and that customer accounts were safe.
The attack method is a near-exact replica of the Binance case. According to Le Monde, hackers took control of the computer of a third party with transaction authority, infiltrated the bank's systems, and withdrew more than €100 million out of the bank's €10 billion (approximately $11.3 billion) in equity capital. The stolen funds were converted into cryptocurrencies and dispersed across multiple exchanges. Kraken, a US exchange, detected an unusually large transfer of funds from a European bank and issued an alert on the 3rd, blocking transactions in progress. The perpetrators have not yet been identified.
Concerns are rising in French financial circles that the vulnerability of traditional banking systems has been exposed. A bank official told Le Monde, "This is a major warning signal for France and the entire European financial sector," adding, "It shows that traditional banks are still exposed to considerable risk."
The Binance incident was a five-month, multi-stage operation by North Korean hackers. They opened with a supply-chain attack in June that lured a Binance wallet development and operations engineer into downloading a tampered development tool. In September, they conducted a fake hiring process targeting an engineer they had approached on a job platform, and in a second-round interview, a person posing as the CEO got the engineer to install malware-laden software on a work computer under the pretext of completing an assignment. Using the infected computer as a foothold, they exploited internal AI tools to obtain control of other engineers and program distribution authentication keys, then on the 29th of last month distributed a program they had created to launch the attack.
The epicenter of this theft was "EIP-7702," an Ethereum wallet upgrade feature. Introduced with the Pectra upgrade in May 2025, this feature grants smart contract execution authority to ordinary wallets that were previously signed with private keys. Once the account holder signs a delegation, it remains in effect until revoked, likened to an automatic payment set up for convenience. The problem is that this delegation can turn into a channel for asset theft.
According to on-chain analysis, the attacker submitted 50 delegation signatures in a single transaction at 8:20:59 p.m. UTC on October 29. All were signatures generated with the key of Binance hot wallet "Binance 14" and pointed to a sweeper contract that scoops up funds. About three minutes later, the sweeper executed, and 167,464 ETH, $1.6 billion worth of USDT, and 63 other types of tokens—worth about $2.5 billion (~3.4 trillion won) at the time—were drained at once. TRM Labs analyzed that the attacker used this authority to issue commands to a separate wallet and withdraw an additional $823 million (~1.1 trillion won) worth of USDC.
The delegation remained in effect for about 3 hours and 50 minutes, until Binance revoked it at 12:10 a.m. the next day. Even during that window, Binance's systems continued to send customer deposits to this wallet, and the attacker swept up the additional deposits in two rounds. Assets on chains without EIP-7702—including 18,270 Bitcoin as well as XRP, Solana, and Tron—were drained through ordinary transfer methods. The amount stolen in connection with this feature is about $3.3 billion (~4.4 trillion won), slightly more than half of the total damage.
Assessments differ on the scope of EIP-7702's responsibility. Ido Ben-Natan, co-founder of security firm Blockaid, pointed to the possibility that the feature was used as a means to sweep funds in bulk and to bypass verification procedures, but assessed that the theft would have been possible even without it. Ivo Georgiev, co-founder of wallet developer Ambire, assessed that the difference is not significant given that the attacker had already obtained signing authority. He warned, however, that even if system control is regained, the risk remains unless the malicious delegation is revoked.
Binance said the laptop of a DevOps engineer was compromised. Co-CEO Richard Teng said additional breach points were found but there was no evidence of private key leakage. How the attacker obtained signatures with Binance's keys has not yet been disclosed. Tether and Circle moved to freeze their stolen stablecoins, and Binance said it had locked up about $3 billion (~4 trillion won) worth with partners. The company said it would bear the losses in full, secured $6.34 billion (~8.5 trillion won), and on the 1st replenished about 95% of the affected assets with its own funds.
South Korea is not a safe zone either. Over the past month, about 473,000 pieces of information were leaked from 37 financial companies, and the amount of funds stolen was estimated at about 1 billion won (approximately $740,000). From the first confirmed breach on September 30 to the 3rd of this month, 40 reports were filed, spanning 4 banks, 5 securities firms, 3 insurers, 5 savings banks, 1 mutual finance company, 2 lenders, 4 online investment firms, 10 electronic financial businesses, and 3 crypto companies. The leaked information includes employee data, customer names, resident registration numbers, and account numbers, but no leakage of information that could be exploited for fraudulent payments, such as account passwords, has been confirmed.
Managed funds were mainly stolen from small crypto exchanges and electronic financial and online investment businesses. The funds were company-managed assets such as internet-connected hot wallets, consumer points, and online investment deposits, but there is no indication yet that this has led to losses for individual users. On the 5th, South Korea's Financial Services Commission held a meeting chaired by Chairman Lee Eok-won with the Financial Supervisory Service, the Financial Security Institute, heads of financial industry associations, and related government ministries to review measures to innovate the security system in the AI era.
Chairman Lee said, "We will not tolerate behavior that causes accidents or amplifies damage through formal inspections and complacent responses, or that leaves known security risks unattended or neglects even basic management," adding, "Serious management failures or negligent responses will be strictly held accountable under relevant laws, extending to executives including the CEO." The authorities plan to handle vulnerabilities found in full inspections flexibly on the premise of immediate remediation, but will take strict action if a breach occurs after an inspection.
This incident has shown that custody ratios alone cannot guarantee safety. The supervisory regulations of the Act on Protection of Virtual Asset Users require exchanges to keep at least 80% of user asset value in cold wallets, but the structure in which a single signature allows malicious code to execute and newly deposited funds are drained until the delegation is revoked shows that a separate response system is needed. On the 2nd, the FSC held an emergency meeting with major exchanges, urging them to increase the cold wallet ratio and set aside additional reserves, and focused on inspecting hot wallet withdrawal approval and signing procedures and administrator authority management. In South Korea, there was a precedent in November of last year when 44.5 billion won (approximately $33.1 million) worth of assets was drained from Upbit's Solana-related wallet. The market expects that the key issues in future financial security regulation will be what requests the signing system permits, whether malicious delegations can be detected and revoked immediately, and whether additional funds can be blocked from flowing into compromised wallets.